



Proxy vs VPN: Differences, Advantages and When to Use Each
At first glance, a proxy and a VPN solve the same problem: placing an intermediary between you and the internet, hiding the source IP address. The similarity, however, ends there. One hides; the other hides and protects. Choosing wrong — or assuming one plays the other’s role — is one of the most common mix-ups we find when reviewing corporate network security.
That is why, in this article, we explain how each technology works, the advantages and limitations of each, and how the pair fits today’s corporate reality, where hybrid work is the norm and remote access has become the door criminals target most.
What a proxy is
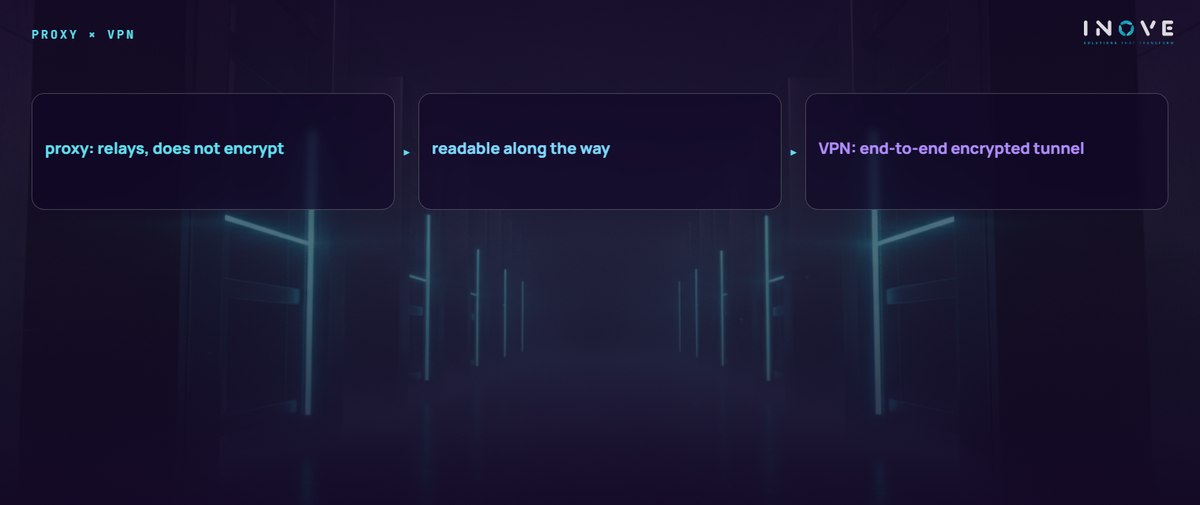
A proxy is an intermediary server between the user and the internet. You request a page, the proxy fetches it on your behalf, and the destination site sees the proxy’s IP — not yours. Simple and efficient for what it sets out to do.
Advantages:
- Basic anonymity — hides the source IP while browsing;
- Control and filtering — in the corporate world, the proxy is what enforces browsing policies, blocks site categories and logs usage;
- Low overhead — with no added encryption, latency tends to be lower, and caching can even speed up repeated access.
Limitations:
- No encryption of its own — the traffic can be read by anyone along the path;
- Limited security — it does not protect against malware or interception;
- Restricted scope — it usually covers only certain applications or protocols, not the whole device.
What a VPN is
A VPN (virtual private network) creates an encrypted tunnel between the device and a trusted server. All traffic travels inside it: besides hiding the IP, the VPN prevents the content from being read along the way — on airport Wi-Fi, at the ISP, at any intermediate point.
Advantages:
- Robust security — end-to-end encryption of the tunnel, for all the device’s traffic;
- Advanced privacy — protection against tracking and interception;
- Remote access to private networks — the classic corporate use: reaching internal systems securely from home or on the road.
Limitations:
- Speed — encrypting and rerouting has a cost; modern protocols have reduced the loss dramatically, but it exists;
- Cost and management — reliable solutions require licensing and administration;
- A valuable single point — a stolen VPN credential gives the intruder the same wide door it gives the user. That is why it demands extra care, as we will see.
Which one to choose — and what changes for the company
The practical rule: to filter and control browsing, a proxy does the job well; to protect data in transit and reach the internal network, the answer is a VPN. In most companies, in fact, the two coexist — each at its post.
Corporate remote access, however, has evolved beyond the pair. Because a traditional VPN grants broad network access, the market is moving toward the Zero Trust model: instead of opening the whole network, each application is released individually, verifying user, device and context on every access. For companies with a large hybrid workforce and critical systems, it is the natural evolution of the infrastructure design.
Good practices for corporate use
- Strong MFA on the VPN — passkeys or FIDO2 keys, never just a password;
- Least privilege — each profile reaches only the systems it needs, even inside the tunnel;
- Updates current — outdated VPN concentrators accumulate actively exploited vulnerabilities;
- Session monitoring — anomalous times, origins and behavior deserve an alert;
- Third-party access reviews — a vendor with a permanent, forgotten VPN is a classic risk.
In short, proxy and VPN each have their place in the arsenal: one organizes and controls browsing, the other protects data in motion and connects the remote team securely. The mistake is not in using one or the other — it is in confusing anonymity with protection, or in treating the VPN as a safe while leaving its own door unlocked. Designing that remote access the right way, from the tunnel to the authentication, is part of what Inove delivers in its cybersecurity practice.