



DevSecOps: 9 Steps to a Secure and Effective Journey
For years, security was the last stage of development: the software would be finished, someone would “run the scanner” and fixes would rush in — when they came at all. DevSecOps flips that logic: security is born together with the code, automated in the pipeline and owned by the whole team, not by a distant department.
That is why, in this article, we organize the journey into nine practical steps, in the order that usually works best. It is the path we follow in Inove’s development projects — and one that has gained urgency now that AI assistants speed up code writing and, with it, the speed at which a flaw reaches production.
The 9 steps of the journey
1. Education and awareness. Before the tooling, the culture. The whole team — dev, ops, QA, product — needs to understand why security is a shared responsibility. Regular training on current threats and secure code review, including code suggested by AI assistants, which demands the same scrutiny as code written by hand.
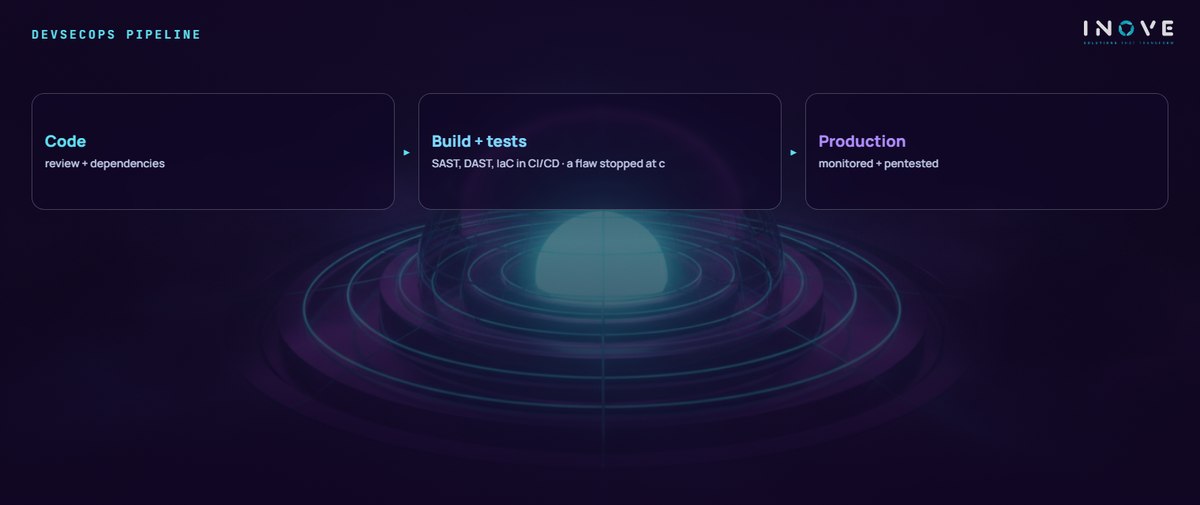
2. CI/CD with security built in. Automate as much of the build and delivery process as possible, with security tests inside the pipeline. The flaw then shows up at commit time, not at incident time — and delivery becomes faster and safer, not one or the other.
3. Continuous vulnerability assessment. Static (SAST) and dynamic (DAST) analysis tools integrated into the pipeline, plus third-party dependency checks. After all, a large share of today’s flaws enters through the software supply chain — the library nobody reviewed.
4. Monitoring and threat detection. In production, centralized logs, intrusion detection and behavior analysis. The goal is shortening the time between suspicious activity and response — from weeks to hours.
5. Security as code. Infrastructure as code (IaC) and security policies versioned alongside the application. Configuration becomes an auditable artifact: reviewed in pull requests, applied identically across all environments, with no undocumented “manual tweak”.
6. Cross-team collaboration. Joint code reviews, threat modeling at the start of every sensitive feature and direct channels between dev, security and operations. Security that only shows up to say “no” at the end becomes the enemy; involved from the design stage, it becomes an ally.
7. Identity and access under control. Least privilege everywhere: pipelines, environments, secrets. Strong MFA for people, secret vaults for systems — an API key committed to the repository remains one of the silliest and most expensive causes of incidents.
8. Regular penetration testing. Automation finds the known; a pentest finds what automation cannot see — broken business logic, chains of small flaws. Dedicated or outsourced teams, testing applications and infrastructure in regular cycles.
9. Continuous learning. Post-incident and post-deployment retrospectives, with security metrics tracked like product metrics: time to fix, vulnerability density, test coverage. What is not measured does not improve.
What changes when security is born with the software
The practical effect shows up on three fronts. First, cost: fixing at the code stage costs hours; in production, it costs an incident — and, under a mature LGPD (the Brazilian data-protection law), sometimes a regulatory notification too. Second, speed: it sounds paradoxical, but teams with automated security ship faster, because they stop less often to fight fires. Third, trust: enterprise customers increasingly audit the delivery pipeline of whoever develops for them; having the answer ready shortens contracts.
In short, the nine steps do not need to be deployed all at once — start with culture and the pipeline, and climb one step per quarter. That is how we structure the pipelines in Inove’s software and application development projects, with the cybersecurity practice closing the loop with pentesting and monitoring. Security that is born with the software does not delay delivery — it is what lets you ship fast without fear.